starclick

Thursday, 3 April 2014

How to speed up SATA hard drives 

Speed up SATA hard drives

In Windows, by default, the advanced write caching feature of SATA hard drives is not enabled. To enable it, write ‘devmgmt.msc‘ in start menu search bar and hit enter to open the Device Manager.
Device manger How to speed up SATA hard drives in Windows 7
In the left side, select Disk Drives and rightt-click on it.
Device manger properties How to speed up SATA hard drives in Windows 7
Open its Properties and go to Policies tab.
Device manger properties 2 How to speed up SATA hard drives in Windows 7
There select Enable Advanced Performance.
Click OK.

Wednesday, 2 April 2014

How to identify unsigned drivers using sigverif utility in Windows XP | 8 | 7

A Device Driver is a program that controls or helps operate a hardware device. When 3rd-party vendors create a new driver, it can be submitted to Microsoft for “Device Signing“. This ensures the quality. To help maintain the integrity of your Windows operating system, critical files are digitally signed so that any changes to these may be easily detected. However, not all drivers are digitally signed, as a result of which some of them may cause system instability.

Identify unsigned & digitally signed Drivers

File Signature Verification Tool or sigverif

Microsoft has a tool in place in Windows 8 | 7 and Windows Vista calledsigverif.exe or the File Signature Verification Tool which helps you identify unsigned drivers.
To access it, type sigverif  in Windows search and hit Enter.
signverif How to identify unsigned drivers using sigverif utility in Windows 8 | 7
Click Start. The program will scan all the device drivers.
signverif utility How to identify unsigned drivers using sigverif utility in Windows 8 | 7
On completion of the scan, it will list down those which are not digitally signed. In my case since all were digitally signed, I received the following message.
sigverif 400x169 How to identify unsigned drivers using sigverif utility in Windows 8 | 7
Should you wish to see the list of all the drivers scanned, Click on Advanced & select View Log.
signverif advanced How to identify unsigned drivers using sigverif utility in Windows 8 | 7
You will be able to view the log.
signverif log How to identify unsigned drivers using sigverif utility in Windows 8 | 7

DirectX Diagnostic Tool or DxDiag.exe

To verify if your Drivers are digitally signed, you can run the DirectX Diagnostic Tool. To do so, type DxDiag.exe in the Search Box and hit Enter. The DirectX Diagnostic Tool is designed to help you troubleshoot DirectX-related issues.
dgx display How to identify unsigned drivers using sigverif utility in Windows 8 | 7
The DirectX Diagnostic tool (DXDiag.exe) gathers information about the system and the DirectX installed components. It also provides a number of tests to ensure that components are working properly. Use the diagnostic tool to create a report about your computer by running Dxdiag.exe and clicking on the Save All Information button.

Wednesday, 5 March 2014

How to Turn On Auto-Complete in the Command Prompt

Do you use the command prompt on a daily basis? If you do, then this tip is definitely for you! I recently found out that there is a way to turn on auto-complete for the command prompt via a simple registry hack. So that means if you are typing in a long path, simply type in the first few letters and then press TAB to auto-complete.
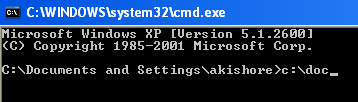
For example, if I am typing in C:\Documents and Settings\, I would just need to type inC:\Doc and then press the TAB key.

enable auto complete command prompt
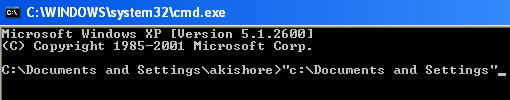
dos prompt auto complete
As you can see, there is only one option that starts with “doc”, so it’s automatically filled along with quotes since it has spaces in the path! Now that’s pretty neat. I always loved using auto-complete in Windows Explorer or even in Open and Save dialogs, but never knew it could be done in the command prompt also.
You can also browse through the different folders and files in a directory by simply pressing the TAB key. So if you type in C:\ and then keep pressing the tab key, you will be able to cycle through all the folders and files in that path in alphabetical order, i.e. C:\Documents and Settings, C:\Program Files\, etc.

How to enable auto-complete for command prompt

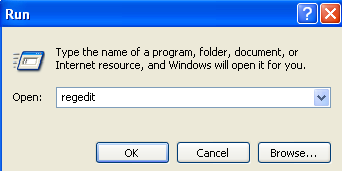
Step 1: Click on Start, then Run and type in regedit
regedit
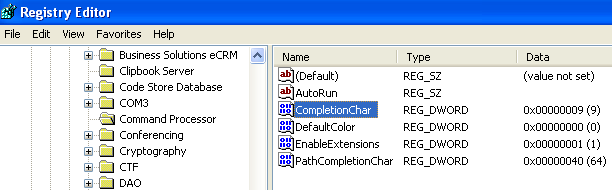
Step 2: Navigate to the following registry key:
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Command Processor
Step 3: Double-click on the “CompletionChar” key and change the value to 9
completionchar
Now close regedit and open the command prompt. Start typing in a partial path and then press TAB to auto-complete it! Pretty sweet eh! Great for anyone who has to work with the command prompt a lot. Enjoy!
1. Search for “Run” from the Windows Start screen and click on it to open its command prompt.
2. Type in “gpedit.msc” and click “OK.”
3. From the main screen of the Local Group Policy Editor, you want to head to the following entry:
Computer Configuration -> Administrative Templates -> Windows Component -> App Package Deployment
4. Right-click on “Allow all trusted apps to install.”
5. You’ll want to enable this entry to all non-Windows Store apps to install in Windows 8. Make sure to click “Apply,” then “OK” to change the entry’s settings.
Before you install any non-Windows Store apps, they still must meet two criteria:
  • The developer must cryptographically sign the app
  • Your computer must be able to accept the certificate
6. If the app meets these two conditions, then you’ll want to use Windows PowerShell to run the following command:
add-appxpackage C:\app1.appx –DependencyPath C:\winjs.appx
“app1.appx” is the app you want to install, you’ll need to change this as necessary depending on how it’s named.
“winjs.appx” is the dependency for the app, which you’ll also need to change if necessary. The dependency will be included with the app.
Now, you’re ready to use your new non-Windows Store app on Windows 8.
Make sure you’re only installing these apps from trusted sources and always keep aWindows 8 system recovery image or backup handy in case you run into issues.

Thursday, 28 November 2013

FSMO
------
flexible single master operations:
All DC can update user db. There is one master domain master, that can operated certian operations. five such operations are
1. schema master (forest role)
2. domain naming master(forest role)
3. RID master(domain role-present in each domain)
4. Infrastructure master(domain role-present in each domain)
5. PDC Emulator(domain role-present in each domain)
1. Schema master  control updates and notifications ( like username group passwords) is the domain controler(dc) that has updated copy of schema(db defination-define how the databse is designed. for example user has UName, UPassword). All other dc are read only. BUT schema master is RW(Read Write). For installing exchange we need eccess to schema master, as exchange will change schema. By default the first dc is schema and domain naming master.
user accounts -stores - user phone no,add,email id etc

computer accounts - stores - computer accounts and groups ,computer name, domain name


2. Domain Naming Master: it checks the domain name configurations, just to make sure that domain names are unique and valid.
3. RID master(Relative Identifier Master): it allocated a pool of mutually exclisive identifier to each dc. Security is based on RID
4. Infrastructure master: is used for intr domain operations to ensure consistency in env, when obj are renamed or when they are moved. its work along with global catolog(gc). Thats why if Infr Master ang gc are on the same server, then infr Master role is switched off, because they performs same role

5. PDC Emulator: ensures that the backward compatibilty is there for BDC(backup domain controler). When we upgrade DC of WinNT to Win2003, then PDC Emulator will provide support

What are the FSMO Roles?

I will talk more about the specific functions of the FSMO roles in the next article in this series. I do however want to quickly mention what these roles are. As you may recall, I mentioned that there are three domain specific roles, and two forest specific roles.
The domain specific roles include the Relative identifier, the Primary Domain Controller Emulator, and the Infrastructure Master. Forest level roles include the Schema Master and the Domain Naming master. Below is a brief description of what these roles do:
Schema Master: maintains the authoritative copy of the Active Directory database schema.
Domain Naming Master: maintains the list of domains within the forest.
Relative Identifier Master: responsible for ensuring that every Active Directory object at a domain receives a unique security identifier.
Primary Domain Controller Emulator: acts as the Primary Domain Controller in domains containing domain controllers running Windows NT.
Infrastructure Master: the Infrastructure Master is responsible for updating an object’s security identifier and distinguished name in a cross domain object reference.

Thursday, 21 November 2013

A Beginner's Guide to DNS 

Since I started a thread on Managed DNS, I figured it would be nice to do a complementary guide to DNS.

So, here is my Starter Guide to DNS (v0.1). It's not all inclussive, so if you think theres something to add... please add it.

Some Definitions

A Domain Name is a human language representation of an IP address.

An IP Address is what every computer on the internet uses to address itself to the other computers on the the Internet (using the network protocol called TCP/IP. IP (v4) Addresses look like 123.123.123.12

When someone types in a domain name like www.domain.com, their browser communicates with a series of root domain name server that act as a dictionary and provides the IP address associated with that domain name. Then the browser can use that IP to communicate to the server that the website is hosted on.


TLD (or Top Level Domain) is the last part of a domain name... the com, net, org, two letter county domains, and the several other TLDs out there.

SLD (or Second Level Domain) is the most human readable part of the domain name. In a domain name like www.domain.com, domain is the SLD. An SLD can have any alphanumeric character in it (a-z, 0-9), dash or minus ( - ), and underscore ( _ ). But it cannot have spaces between characters.

Sub-Domain (also called third level domains) are technically called Canonical Domains (or CNAMEs) for short. Sub-Domains are like having an extra domain name and can be almost anything you like. In a domain name like subdomain.domain.com, subdomain is the sub-domain.                                                       It works the same as a regular domain name.

A-Records (or Address Record) is the basic and most important DNS record. A-records point to an IP address. Your short domain name (without the www), NS, and FTP should have A-records. Subdomains sometimes have A-Records too. A-records can point to any IP-address.

CNAME-Records (or Canonical Domains) include subdomains and Aliases, CNAMEs are used to point to a domain name or to a file in a domain. However, CNAMEs should always point to an A-record, not another CNAME. It is a common practice to create a CNAME for www and for subdomains that are actually hosted by your domain. CNAMES can also be used as temporary aliases to point your domain to another domain.

Note: when pointing a CNAME, always put a period after the domain (ie: ftp -> CNAME -> domain.com.)

MX-Records (or Mail Exchange) point to the name of an email server and holds a preference number for that server. MX-records must point to an A-record or in some situations an IP-address.


Example DNS Record:


Code:
Host Name          IP Address/URL          Record Type 

@                  123.123.123.12          A-Record
www                domain.com.             CNAME

ftp                123.123.123.12          A-Record
mail               123.123.123.12          A-Record
ns1                123.123.123.12          A-Record
ns2                123.123.123.13          A-Record
subdomain1         domain.com.             CNAME
subdomain2         domain.com.             CNAME     

MX-Record: mail -> domain.com. -| Preference = 10     


@ is short domain (domain.com)
Put period after domain name

DNS Record Types

Most of the time, when someone talks about a DNS record, they are referring to the simple "directory enquiries" way of mapping a computer's name to its IP address, but this isn't always the case. The DNS can be used to find out other information as well by using different DNS record types.

Common DNS Record Types

  • NS – specifies which are the DNS servers for your domain;
  • A – specifies IP addresses corresponding to your domain and its subdomains;
  • MX – specifies where the emails for your domain should be delivered;
  • CNAME – specifies redirects from your domain’s subdomains to other domains / subdomains;
  • SPF – Sender Policy Framework (SPF)
A
An A record translates a computer's name to its IP address. Sometimes it may translate to multiple IP addresses when there are many computers perfoming the same role.
gondolin.org.uk A 173.254.28.64
AAAA
An AAAA is the IPv6 version of a A record. This is the future. For now, almost everyone still uses IPv4, so you won't see this much.
Techy note [+]
archive.ubuntu.com AAAA 2001:67c:1360:8c01::1a
PTR
A PTR record translates a computer's IP address to its name. In many cases the A record and PTR record for any machine on the Internet will match (just lookup one to find the other). In practice, the PTR record is often forgotten (which can cause occasional problems) or gives the name of the host computer (in cases where multiple services live on the same computer, as in the example below).
Techy note [+]
173.254.28.64 PTR just64.justhost.com.
MX
An MX record returns the name of the mail server (or servers - there can be more than one) for a domain. This is mainly used by other mail servers so that they know which machine they should deliver outgoing messages to.
MX, or mail exchange, records describe the machines to contact in order to send mail to a given DNS node
Techy note [+]
ubuntu.com MX 10 mx.canonical.com

                 
norbert.dept1.cornell.edu86400A128.253.180.254
norbert.dept1.cornell.edu86400MX10mailhost.dept1.cornell.edu
          
          norbert.dept1.cornell.edu86400MX20mailhost2.dept1.cornell.edu

          norbert.dept1.cornell.edu86400MX30mailhost3.dept1.cornell.edu
NS
This returns the names of the name servers for a domain. Most of the time there should be more than one of these. It is this that allows one name server to refer you to another when needed (e.g. looking up details in a subdomain)
ubuntu.com NS ns1.canonical.com
ubuntu.com NS ns2.canonical.com
TXT
The TXT record stores general-purpose text. Originally this was used for descriptions and other helpful information, but nowadays it is also used to store information for specific services (e.g. the SPF email anti-fraud system) 
slashdot.com TXT "SourceForge, Inc."
 
CNAME
A CNAME record provides a way to give an alias to a host name, typically used to give friendly names for computers with hard-to-remember ones or to provide service names (like "mail" or "www")
www.gondolin.org.uk CNAME gondolin.org.uk
SOA
                 
                  The SOA resource record is always the first record in a DNS zone. Set the Primary Server to your primary nameserver
This one is a bit special and not something many people really need to worry about. SOA stands for "start of authority" and it exists in every single Internet domain, providing information used by other name servers to ensure they carry up to date information about the zones they manage.
Techy note [+]
gondolin.org.uk SOA ns1.pipedns.com. root.cl18.justhost.com. 2013021101 86400 7200 3600000 300
Just to add an extra level of complexity, most of the above types can have more than one value. For example, an MX record can list multiple mail servers along with a preference value to indicate in which order they should be contacted (try one and if it doesn't answer try the next on the list).

Every Admin Should Know These Commands Active Directory 1.   To quickly list all the groups in your domain, with members, run this c...